Compliant iGaming content across 14 markets
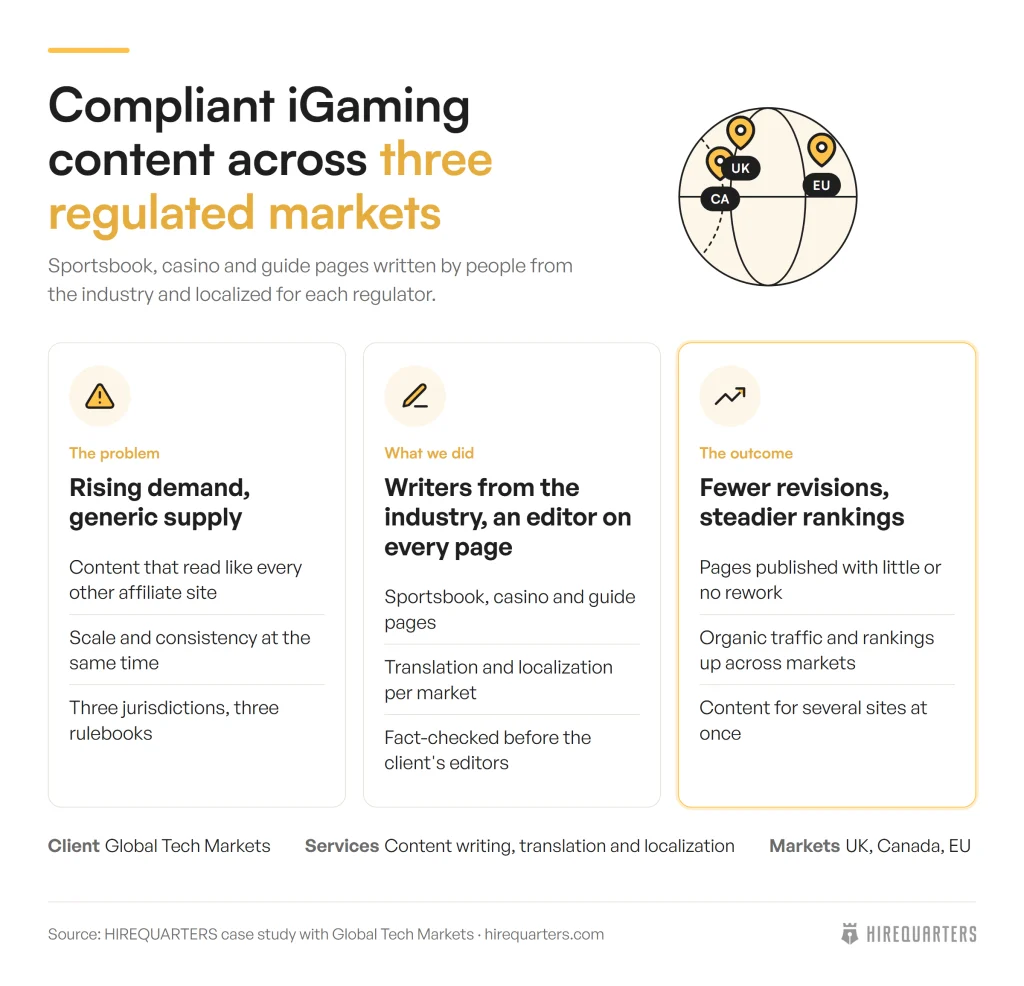
We gave an iGaming marketing company writers from the industry and translators for each market, so its brands kept publishing across 14 markets without generic copy or compliance risk.
View case study
We gave an iGaming marketing company writers from the industry and translators for each market, so its brands kept publishing across 14 markets without generic copy or compliance risk.
View case study
We gave a Webflow enterprise agency extra editorial capacity so its team could keep delivery moving across SEO, growth, and client production work.
View case study
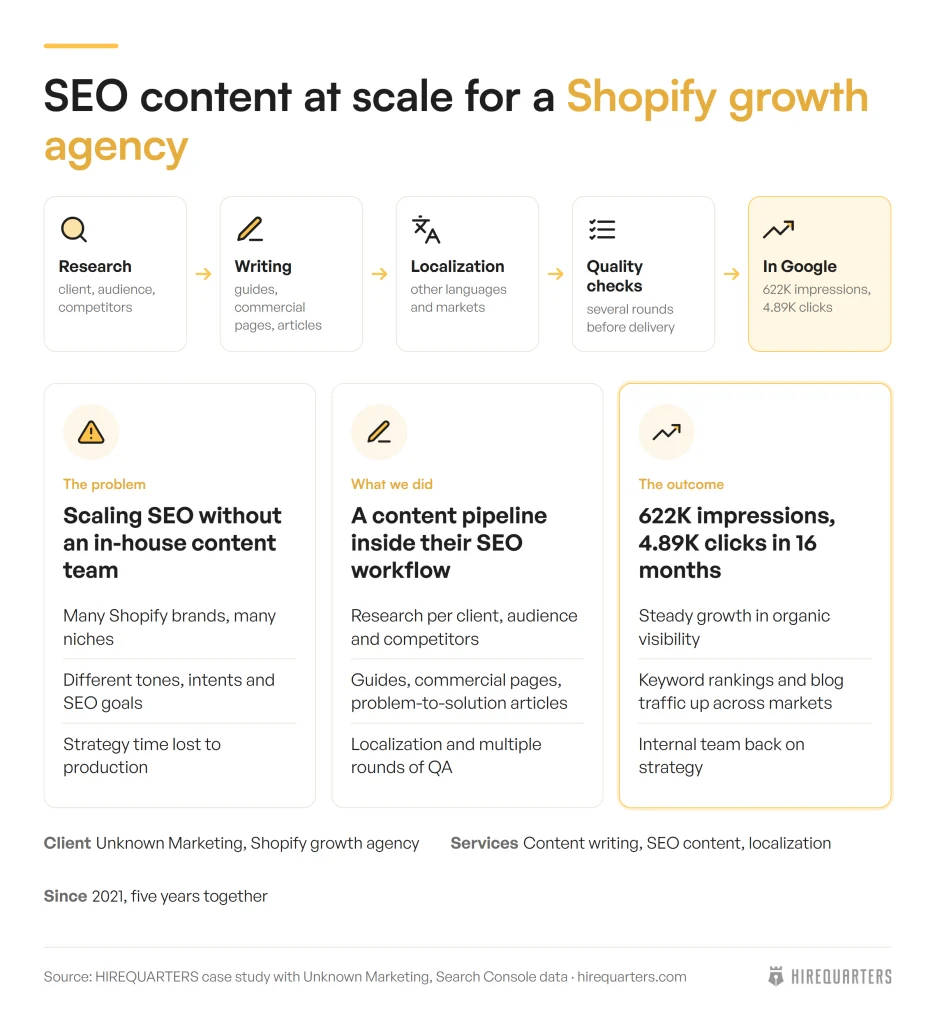
We became the content pipeline for a Shopify growth agency with no in-house writers: guides, commercial pages and localized pieces across every client niche, with 622K impressions and 4.89K clicks in sixteen months.
View case study
At HIREQUARTERS, we define cybersecurity SEO as competing in a niche with competitive search engine results pages (SERPs), compliance-driven search intent, and a tech-savvy audience who can spot thin pieces from a mile away.
We’ve been in the game since 2017, long enough to see how generic search engine optimization (SEO) practices can damage cybersecurity companies’ reputations. Throughout 2025 and 2026, we saw that happen across the industry through surface-level writing, keyword stuffing, and references to expired compliance frameworks.
Our approach is different. HIREQUARTERS writers understand security threats, tooling, and frameworks to their core and primarily serve as an extension of your internal team. We handle research, writing, and optimization while your engineers focus on the product, so your pages can withstand high scrutiny and rank for the queries your buyers are actively searching for.
Our security content marketing services serve security Software-as-a-Service (SaaS) brands, Managed Detection and Response (MDR) providers, and Managed Security Service Providers (MSSPs). We also work with Identity and Access Management (IAM) vendors and compliance tooling makers, helping them explain their products to buyers with specific requirements. Cybernews, which we have written for since November 2024, drew an estimated 903,000 organic visits in October 2026, up from 633,000 in October 2025 (Ahrefs, November 5, 2026).
One client, a global cybersecurity media outlet that has chosen to remain anonymous, set the task in one line: “SEO organic content at a global scale, without a single drop in quality.” Our cybersecurity case study dives into how we solved that problem and what the work entailed.
Before they commit to a product, security buyers must first understand how it fits their needs and workflows, and that’s where HIREQUARTERS comes in. We turn your SaaS documentation into product pages, guides, blog posts, reviews, and comparisons that cater to security teams without overwhelming non-technical decision-makers.
Enterprise security buyers are skeptical and often take months to evaluate a product. We cater to this trust-first audience by producing threat hunting and incident response pieces, service pages, technical guides, blog posts, and other content that in-house teams respect and enterprise buyers trust. Everything is also tailored to long sales cycles and compliance drivers.
Security buyers don’t look for vendors; they search for solutions. That creates a gap between intent and vendor pages, but it’s also one we can bridge. At HIREQUARTERS, we map buyers’ problems, such as passwordless sign-in or Privileged Access Management (PAM) for Kubernetes, to your pages that show how your product solves the issue.
Chief Information Security Officers (CISOs), security architects, and IT leads dislike generic SEO writing, which is often filled with misleading compliance claims. We tread carefully.
To avoid triggering regulatory and trust issues, we produce practical product content that helps buyers prepare for an audit or explains evidence collection without suggesting software alone can guarantee compliance. That also includes guides that define controls and audit terms the way assessors actually use them.
Security buyers use established cybersecurity frameworks to create a common language for measuring risk and verifying compliance. While frameworks like SOC 2, ISO/IEC 27001, and NIST CSF 2.0 and laws like the GDPR are the gold standard across the board, each also attracts a different audience and requires a different page type.
| Framework | Who asks about it | Page type that wins | Our review step |
|---|---|---|---|
| SOC 2 | Security assessors, IT auditors, procurement teams | Trust-first explainers built around the five criteria (see below) | Writers map each claim to Trust Services Criteria. |
| ISO 27001 | CISOs, security leads, compliance managers | Certification pages and readiness guides | Editors check control references against ISO 27001:2022. |
| NIST CSF | Security architects, CISOs mapping tools to risk management outcomes | Implementation guides that map your product to the six functions (see below) | Writers confirm function mapping against your technical documentation. |
| GDPR | Data protection and privacy officers and legal teams | Explainer pieces related to the product’s data protection features | Editors check privacy claims against legal enforcement updates. |
The American Institute of Certified Public Accountants’ (AICPA’s) System and Organization Controls (SOC) 2 is the primary security assurance report enterprise buyers ask for first when evaluating B2B and SaaS vendors. These audits are built around AICPA’s five non-financial categories from 2017, known as the Trust Services Criteria: security, availability, processing integrity, confidentiality, and privacy, whose focus areas were revised in 2022.
The Information Security Management System standard, a joint effort by the International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC) known as ISO/IEC 27001, is also crucial. Its 2022 revision reduced the Annex A control list from 114 to 93, and organizations certified under it had until October 31, 2025, to transition.
For organizations that find ISO/IEC 27001 too rigid, the National Institute of Standards and Technology (NIST) Cybersecurity Framework (CSF) offers a more flexible, outcome-based way to organize security controls. In February 2024, NIST released CSF 2.0, which adds the Govern function to the existing five: Identify, Protect, Detect, Respond, and Recover.
Jurisdiction also matters for security buyers. For SaaS brands, for example, the Federal Trade Commission (FTC) fines companies for unproven performance and fake reviews. But in cybersecurity, vendors must comply with the European Union’s General Data Protection Regulation (GDPR) and the United Kingdom’s GDPR laws.
More importantly, while the former is enforced decentrally, the latter is controlled by one authority: the Information Commissioner’s Office (ICO). And as an example, under the ICO Data Protection Fining Guidance from 2024, the higher maximum amount for an infringement is £17.5 million or 4% of total worldwide annual turnover, whichever is higher, the same two-tier structure as the EU GDPR’s €20 million or 4%.
Cybersecurity content at HIREQUARTERS starts with domain experts drafting the piece, then moves through fact-checking and polishing, and is handed off to your subject-matter expert (SME) for technical and compliance review. The process also aligns with Google’s helpful content guidance update from December 2025, which encourages accurate authorship bylines.
Every HIREQUARTERS-produced piece comes from a writer with real industry experience who knows it’s “SOC 2 Type II audited,” not “SOC 2 certified.” They research every topic extensively, comb through documentation, and try out products before writing the first draft.
The writers also cite common vulnerabilities and exposures (CVEs), with details from vendor advisories, and never resort to fear-, uncertainty-, and doubt-based (FUD-based) tactics.
Once the writer’s done, our editors with years of cybersecurity experience step in. They read the piece cold, just like a security buyer would, to ensure it’s grammatically correct and free of any FUD-based marketing tricks. They then check framing, claims, and sources, and whether the content aligns with all necessary frameworks and compliance rules.
No piece gets published before your SME reviews the polished draft for technical accuracy. The goal here is to confirm that the described product features, behaviors, and configurations match reality, as well as to flag anything that might read wrong to tech-savvy buyers. We also adjust batches to the number of pieces your engineers can handle to avoid swamping internal teams.
HIREQUARTERS is a full-fledged cybersecurity content marketing agency that does more than just SEO. We offer a broad range of services for security vendors, and you can bring us in for a single thing or let us handle your entire strategy through these:
We can talk about writers and editors who understand terminology, threats, CVE identifiers, and compliance frameworks all day, but we’d rather show you our work in action.
Our cybersecurity case study involves an independent global media outlet that covers data breaches, digital threats, and online privacy. The client, which chose to remain anonymous, focuses on delivering investigative security journalism and wanted organic content at scale without it affecting quality.
We answered the call by building a framework-aware content engine. Our SME writers ensured every piece, be it a product review or a comparison guide for readers considering security software, was thoroughly researched and objectively explained each tool’s capabilities. Editors then checked every claim and adjusted the copy to match the publication’s standards.
Our client ended up with drafts ready to publish with minimal effort, giving the internal team more time to focus on projects, threat research, and investigative journalism. The table below shows the figures:
| Case study | Numbers | Broader HIREQUARTERS portfolio | Numbers |
|---|---|---|---|
| Relevant query rankings | Articles regularly ranked in the top five on Google | Words delivered | 10,000,000 |
| Compliance frameworks aligned | 8+ | Sites supported | 200+ |
| Cybersecurity client | Anonymized at its request | Pages shipped | 5,000+ |
| Client’s media organization size | 200+ employees | Rich results earned | 400+ |
The price of our cybersecurity content writing services, or any other work in this niche, depends entirely on the scope of work you’d like to delegate to us.
For example, four 1,500-word pages per month range between $750 and $1,000 as of November 2026. Meanwhile, the standard ongoing growth and maintenance package for a 100-page website that covers three markets costs between $2,400 and $3,100 per month.
You can see what your project costs using our interactive cost calculator. It’ll give you a price range as soon as you select the cybersecurity industry and the services you want to hire us for, be it writing, SEO, GEO & AIO for ranking stability, content operations, or a mix of what we offer.
If you’re still not sure about pricing, you can also just tell us what you need, and we’ll schedule a call within 48 hours. Within a week, you’ll get a written plan if you still want one, and it’ll include exact prices for the specific services you need.
Before you partner with any cybersecurity SEO agency, thoroughly vet the company, its SME writers and editors, and its previous work. These checks apply whether you’re considering HIREQUARTERS as your potential partner or any other agency, and below are a few critical questions you should ask during the evaluation:
| What to ask | What a good answer should look like |
|---|---|
| Which security vendors have you already worked with? | Even with confidential clients, the agency should be able to describe the product and, if possible, show deliverables without compromising anonymity. |
| Can your writers handle feedback from tech-savvy engineers? | Tech-savvy teams should produce drafts that come back from your SME reviews with minor edits, not full-on rewrites. |
| How well do you know the frameworks our buyers are actively searching for? | Knowing of SOC 2 and NIST CSF isn’t enough; teams should be able to explain what all relevant frameworks mean and how they affect pages and phrasing. |
| Can you provide case studies with real figures and periods for review? | High-quality case studies you can trust will always have exact numbers and the dates they cover, even if the clients are anonymous. |
| What will our engineers need to review once your writers and editors are done? | SMEs should supply sources and flag product configurations and claims that only your engineers can confirm. |
Vetting is a two-way street, and our experience has shown us that we won’t be a good cybersecurity content marketing agency for you if you:
If our answers held up and HIREQUARTERS survived your vetting process, tell us about your product, who your target audience is, and what frameworks they search for today. We’ll schedule a call within 48 hours and have a written plan with prices ready for you within a week.
We start with a short call to understand what matters most to your business. Together, we define clear targets and map the best route to reach them quickly and sustainably.
We analyze what your audience searches for and who’s earning their clicks. This helps us spot opportunities, understand intent, and identify where your brand can win visibility.
We group keywords by business value and build a 90-day content roadmap. You get a clear publishing cadence with defined priorities, deadlines, and outcomes you can track.
Writers with domain expertise handle the first drafts, while editors fact-check and polish every piece. The result is conversion-ready content that you can trust.
We optimize titles, headings, FAQ, and CTAs, then connect pages into logical, intent-based paths. This strengthens site structure, improves user engagement, and boosts search visibility.
We secure relevant, audit-safe placements and brand mentions that build long-term credibility. No gimmicks or spammy tactics, just sustainable authority that ranks and lasts.
We track performance through GA4 and GSC, refine what works, and scale proven strategies. Every month, your content becomes sharper, stronger, and more consistent.
We became the content pipeline for a Shopify growth agency with no in-house writers: guides, commercial pages and localized pieces across every client niche, with 622K impressions and 4.89K clicks in sixteen months.
View case study
We gave an iGaming marketing company writers from the industry and translators for each market, so its brands kept publishing across 14 markets without generic copy or compliance risk.
View case study
We helped a crypto and online trading brand produce careful, compliance-aware content for a sector where accuracy and wording matter.
View case study
A cybersecurity SEO agency is a dedicated marketing firm that helps security vendors, Software-as-a-Service (SaaS) companies, Managed Service Providers (MSPs), Managed Security Service Providers (MSSPs), and Managed Detection and Response (MDR) providers improve their visibility on traditional search engines and Google AI Overviews.
Yes, we map content and tailor terminology to frameworks your buyers actually search for, including AICPA SOC 2, ISO/IEC 27001, and the NIST Cybersecurity Framework (CSF) 2.0, as well as the European Union’s GDPR and California’s CCPA laws.
We avoid generic cybersecurity content by moving away from broad topics and zeroing in on specific threats and real configurations. Instead of rehashing basic online hygiene practices like “use strong passwords,” every piece we produce brings something new to the table, as we focus on real-world scenarios and actual adversary patterns and behaviors.
Accuracy at volume depends on product access and a fixed review step. We work from your documentation, a product demo, and time with an engineer for questions, and we check every draft before it reaches your team. Batches are sized to what engineers can review.
Cybersecurity content writing services typically come with a per-piece pricing model. Research reports and technical guides cost more than standard product pages because they take up more time, and case studies and technical whitepapers go even further. Start with our interactive cost calculator or send us your brief anytime, and we’ll get you a per-page range within two working days.
Tell us your goals; we’ll take care of the roadmap.